Secure internal reporting to support NIS2 compliance
Strengthen incident handling, supplier oversight and cyber hygiene with a confidential channel where employees, contractors and suppliers can raise security concerns early — whilst there is still time to act.
Why organisations choose Whistlelink
- Certified to ISO/IEC 27001 — your supplier assessment starts from a documented baseline
- All data hosted in the EU, encrypted in transit and at rest
- Designed for compliance, security and HR teams
- Easy to implement and scale across countries
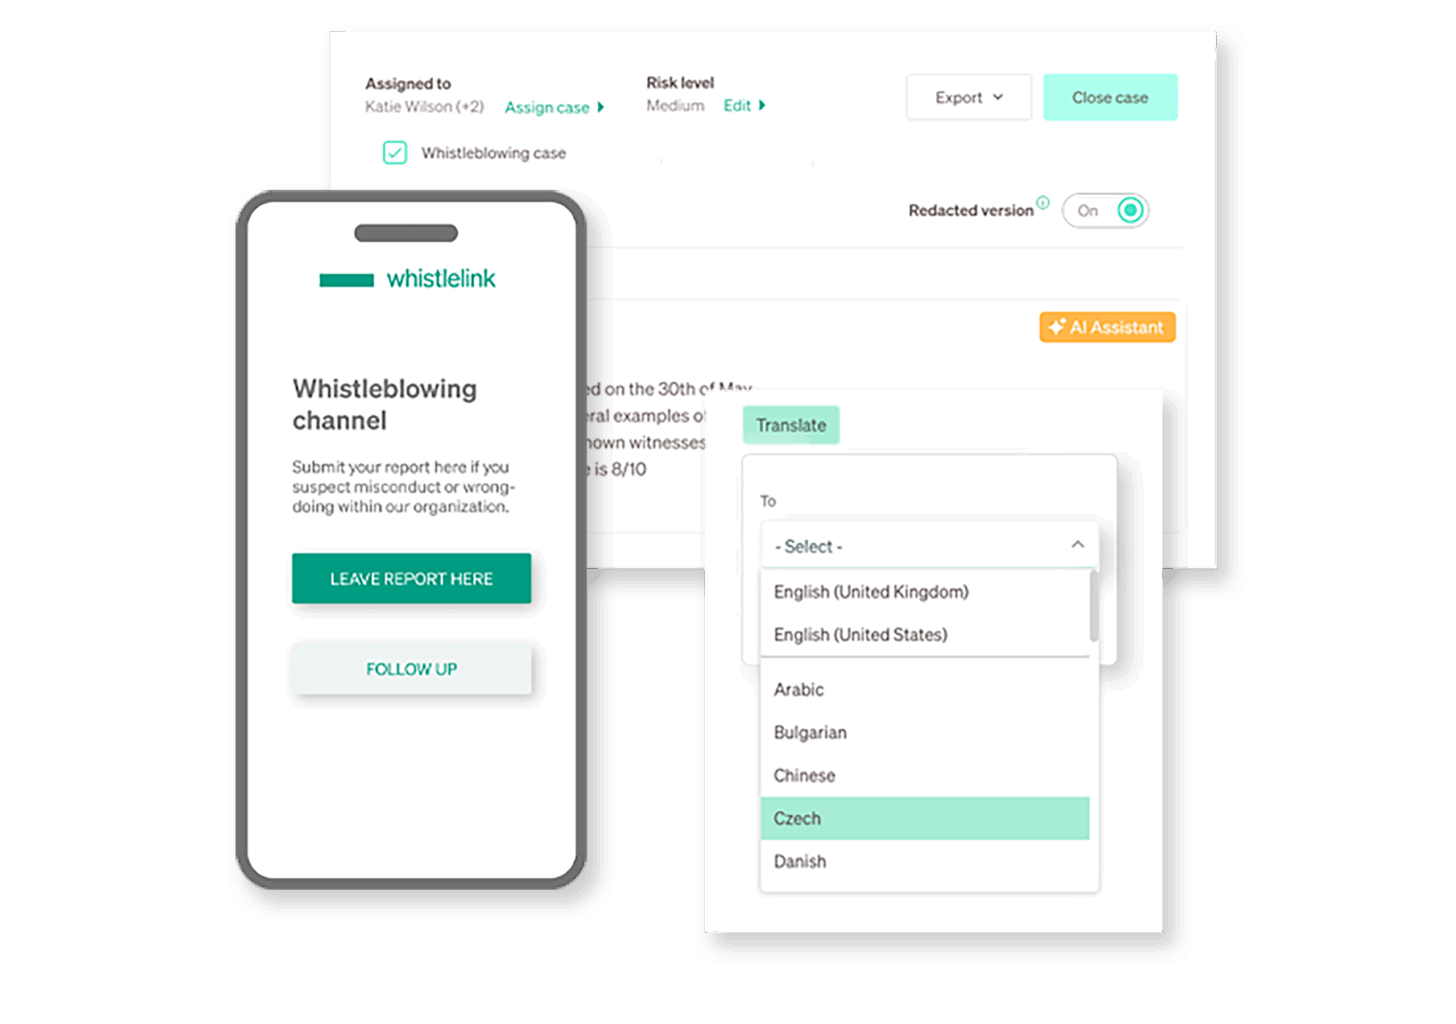
Where NIS2 and internal reporting meet
NIS2 does not require a whistleblowing channel. It requires that you detect, handle and report significant incidents quickly — and it makes the security of your direct suppliers your concern.
You cannot report in 24 hours what nobody told you about. The person who notices the shared credentials, or the supplier quietly failing its obligations, is usually an employee — and they speak up only when it is safe and easy.
A confidential channel evidences two of the Article 21(2) measures: incident handling, and human resources security. And it is already on your compliance map — the EU Whistleblowing Directive covers security of network and information systems, so someone reporting a NIS2 breach is a protected whistleblower whether or not you gave them a route.
For compliance, risk and security teams
NIS2 asks you to show that measures exist and work, not that they were written down.
- Give employees, contractors and suppliers a confidential route to flag security concerns before they become incidents
- Document how each report is received, investigated and resolved, with a complete audit trail
- Feed early signals into incident handling whilst the 24-hour and 72-hour deadlines still allow a considered response
- Extend visibility into your direct suppliers, whose security Article 21(2)(d) makes part of your own
For HR and people teams
NIS2 puts people inside the security perimeter: basic cyber hygiene, training and human resources security sit in the same list as cryptography and access control.
- A safe route for concerns about credential sharing, policy breaches and insider risk
- Protection from retaliation for the person who reports, as the Whistleblowing Directive requires
- Confidential, consistent handling of security matters that involve a colleague or a manager
- Support for the cyber-hygiene and awareness culture Article 21(2)(g) asks for
For leaders and management
Article 20 makes this personal. Management bodies must approve the risk-management measures, oversee their implementation, can be held liable for failures, and are required to follow training themselves.
- Demonstrate documented oversight of how security concerns reach you
- Gain visibility into risks across sites, subsidiaries and suppliers
- Show supervisory authorities a functioning process rather than a policy
- Reduce exposure to penalties that, for essential entities, start at a national maximum of at least €10 million or 2% of worldwide annual turnover, whichever is higher
The NIS2 reporting clock
The clock starts when you become aware of a significant incident — not when you understand it.
from becoming aware to the early warning
from becoming aware to the full incident notification
from the incident notification to the final report
NIS2 or DORA?
Both raise the bar on ICT risk, and the line between them matters. NIS2 is a directive, so it reaches you through national law — in Sweden, cybersäkerhetslagen (2025:1506), in force since 15 January 2026. DORA is a regulation that applies directly to financial entities, and for those entities it takes precedence. If you are a bank, insurer, investment firm or payment institution, start with DORA.
Let's talk!
Want to strengthen incident handling and see security risks across your organisation and your suppliers sooner?
Let’s explore how Whistlelink can support your reporting processes and help you meet NIS2 expectations with confidence.
Annelie Demred