Secure internal reporting for financial entities under DORA
Support your ICT risk governance with a confidential channel where employees, contractors and providers can raise concerns — and cover the internal reporting duties financial regulation already places on you.
Why organisations choose Whistlelink
- Certified to ISO/IEC 27001, with regular penetration testing — evidence for your ICT third-party assessment
- All data hosted in the EU, encrypted in transit and at rest
- Designed for compliance, risk and ICT teams
- Easy to implement and scale across countries
Where DORA and internal reporting meet
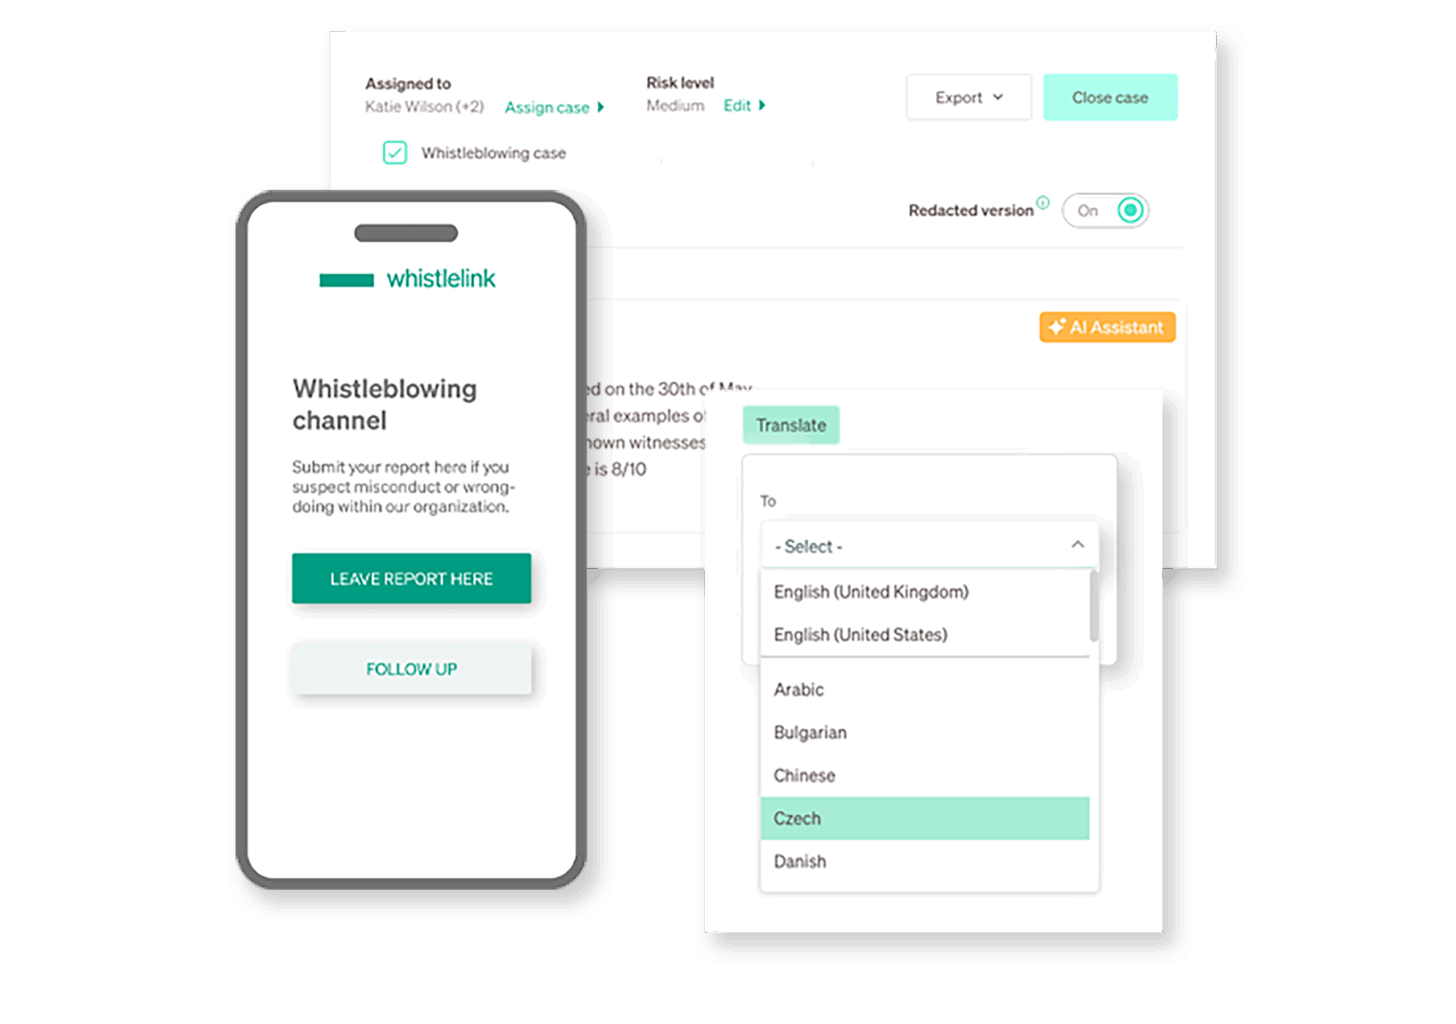
DORA contains no whistleblowing provision — its reporting runs from the entity to the competent authority, on deadlines measured in hours.
Financial entities are not starting from zero, though. An internal reporting channel is already required under the Market Abuse Regulation, the Capital Requirements Directive, MiFID II and the anti-money-laundering rules — the last of which specifies an anonymous channel.
What DORA changes is what has to reach management quickly: ICT weaknesses, failed controls, and how your critical third parties are performing. The channel you already need is the one best placed to carry it.
For compliance, risk and ICT teams
DORA expects ICT risk to be identified, classified and escalated on a clock.
- Capture early signals about ICT weaknesses, workarounds and provider failures before they become major incidents
- Shorten the path from someone noticed to the incident is classified, whilst the four-hour and 24-hour deadlines still leave room to act
- Keep one auditable record of how each concern was received, assessed and resolved
- Cover the internal channel your sectoral rules already require, in the same system
For HR and people teams
Resilience depends on people being willing to say that something is not working.
- Safe reporting for employees, contractors and the staff of your ICT providers
- Anonymous reporting, as the anti-money-laundering framework requires
- Confidential handling of sensitive concerns, with protection from retaliation
- Support for the awareness and resilience training your programme already runs
For leaders and management
Article 5 places ultimate responsibility for ICT risk on the management body. That responsibility is only as good as the information reaching it.
- Demonstrate a working route for concerns to reach the management body
- Strengthen third-party oversight alongside your register of information (Article 28(3)) and your contractual rights (Article 30)
- Show supervisors documented governance rather than intentions
- Build confidence with clients, auditors and supervisory authorities
The DORA reporting clock
Once an incident is classified as major, the clock starts — long before anyone has the full picture.
from classifying an incident as major to the initial notification
from the initial notification to the intermediate report
from the intermediate report to the final report
Covered by DORA or NIS2?
Many organisations are asking the wrong question first. NIS2 reaches you through national law; DORA applies directly and, for financial entities, takes precedence over the national NIS2 rules — Finansinspektionen has confirmed this for cybersäkerhetslagen. Your ICT providers may sit under NIS2 even where you sit under DORA.
Let's talk!
Want to strengthen your ICT risk governance and show supervisors that concerns actually reach the management body?
Let’s explore how Whistlelink can support your internal reporting and help you meet DORA expectations with confidence.
Annelie Demred