Secure whistleblowing to support your ISO/IEC 27001 ISMS
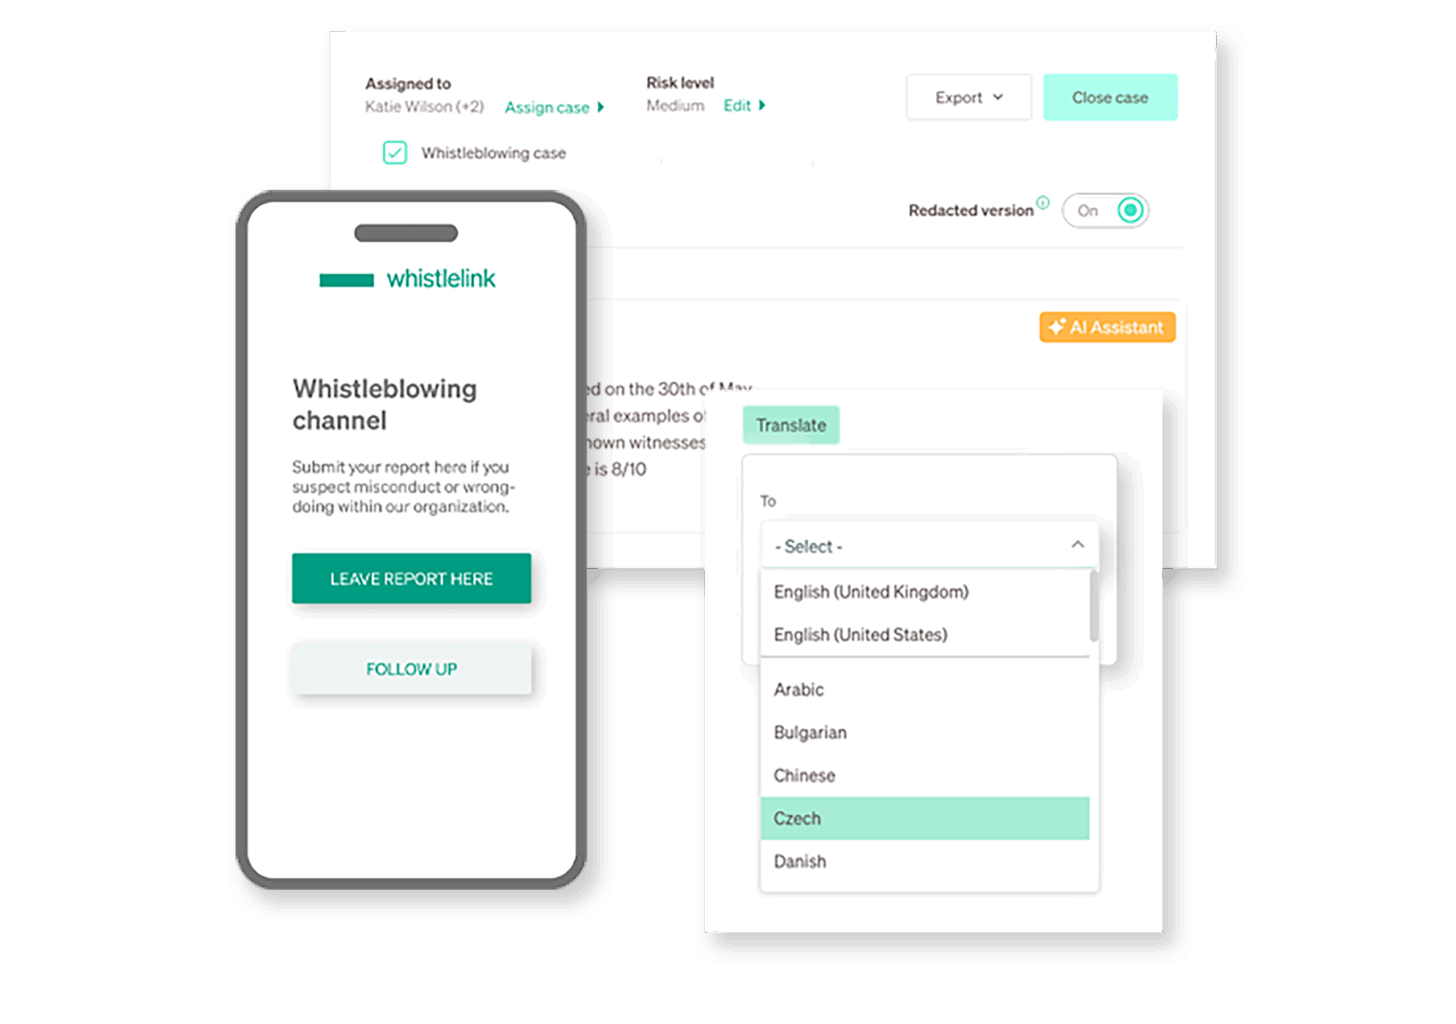
Annex A control 6.8 asks that personnel can report observed and suspected information security events through appropriate channels, in good time. Whistlelink gives them one they will use.
Why organisations choose Whistlelink
- Certified to ISO/IEC 27001 — the same standard you are evidencing
- All data hosted in the EU, encrypted in transit and at rest
- Designed for compliance, security and HR teams
- Easy to implement and scale across countries
Where ISO/IEC 27001 and internal reporting meet
Annex A 6.8, Information security event reporting, asks that personnel can report suspected security events promptly, through appropriate channels. It does not require the channel to be anonymous — a form or a mailbox satisfies it.
What a mailbox does not solve is the event involving a manager, a colleague or a supplier, where the person who noticed weighs up what reporting will cost them. Those are the events that stay unreported longest.
An anonymous, structured channel exceeds the baseline of 6.8 and ties it to the controls around it — awareness training, the disciplinary process and management responsibilities.
For compliance, risk and security teams
Certification turns on evidence. A control that exists on paper but has no records behind it is the one the auditor asks about.
- Offer a reporting route that works even when the event involves someone internal
- Evidence Annex A 6.8 with timestamps, case history and documented outcomes
- Give auditors a clear view of how events were received, assessed and closed
- Keep security event reporting and the rest of your speak-up process in one system
For HR and people teams
Control 6.8 sits in the middle of the people controls, not the technical ones.
- A channel employees trust enough to use before an incident becomes serious
- Confidential handling that protects the person reporting
- A consistent bridge between security events and the disciplinary process (6.4)
- Reinforcement for the awareness training under 6.3
For leaders and management
An ISMS is judged on whether it improves. The events nobody reports are the ones your management review never sees.
- Show the certification body a reporting mechanism that is used, not just defined
- Gain visibility into the events that never reach the service desk
- Support continual improvement with real data on what people are seeing
- Extend the same channel to suppliers and contractors within your ISMS scope
ISO 27001 and NIS2
ENISA’s technical implementation guidance maps the NIS2 cybersecurity risk-management requirements to ISO/IEC 27001:2022 and 27002:2022, so an existing ISMS gives you a substantial head start. ENISA is explicit that the mapping is not a measure of equivalence: certification supports your case, it does not by itself demonstrate NIS2 compliance.
Let's talk!
Want to give your people a reporting route they will actually use, and evidence Annex A 6.8 when the auditor asks?
Let’s explore how Whistlelink can support your ISMS and strengthen the way information security events are reported and resolved.
Annelie Demred